Cloud, DevOps & Security
Penetration testing that finds the gaps and proves they're fixed.
For software teams facing a customer security questionnaire, an audit or a launch, who need to know where they're exposed. Under written authorization and an agreed scope, we test your web apps, APIs and cloud configuration to OWASP methods, explain every finding in plain language, help you fix it and retest to confirm it's closed.
- A person replies within one business day
- A plan you can act on
- You own every asset
- Time to first results
- Testing window of 1 to 3 weeks
- Engagement
- Fixed-price test with a retest included
- Scope
- Web apps, APIs and cloud configuration
- Methods
- OWASP WSTG, OWASP Top 10 and CIS Benchmarks
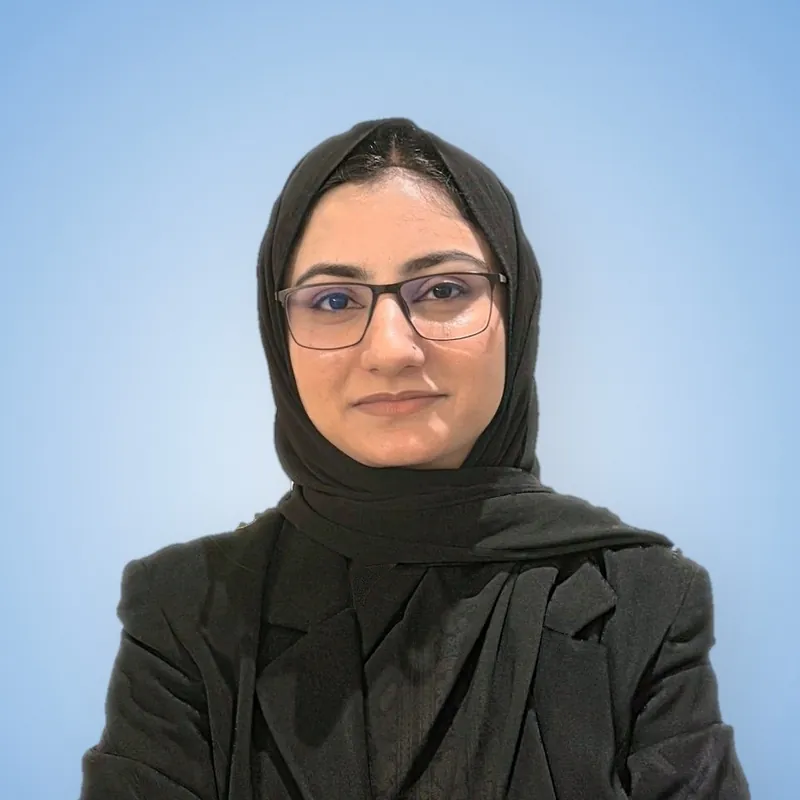 Reviewed by Noor Khan
Pen test· Authorized · retested
SampleThe system owner signs a written authorization, the test checks each target and finds the orders API showing one user another's orders, a fix adds an owner check in the code, and the retest confirms it passes.
- Test authorized in writing
- Scan finds a gap
- Fix is shipped
- Retest passes
Illustration with sample data. Your version uses your accounts and numbers.
Brands Noor has worked with
Overview
What are penetration testing services?
Penetration testing services are authorized, simulated attacks on your applications, APIs and cloud setup, carried out by security testers to find weaknesses before a real attacker does. Testing follows an agreed scope and recognized methods such as the OWASP Web Security Testing Guide. Noorscale delivers a report ranked by risk, a remediation plan your developers can act on and a retest that confirms each fix.
See it in action
What does a penetration test look like when it's working?
When a penetration test is working, you see four changes: evidence for security reviews, real risks found and fixed, developers who know what to change and security that keeps pace. The live sample below is built with illustrative data. Your version runs on your own accounts and your numbers.
Site rebuild · speed and quality
SampleBefore the rebuild: performance score 38, largest contentful paint 4.9 seconds.
Back to full strength, sooner.
Same-week assessments with senior physiotherapists.
Book a visitNext available, Thursday
Same-week slots open
Sports injuries
Back and neck pain
Post-surgery rehab
Lighthouse, mobile
Template and page builderPerformance
Accessibility
Best practices
SEO
- LCPMain content visible
- 4.9 sPoor
- INPResponse to a tap
- 380 msNeeds work
- CLSLayout shift
- 0.21Needs work
Route to a bookingContact page, 7-field form
Page load waterfall
Request Largest element
- HTML document48 KB, no caching
- Stylesheets6 files, 410 KB
- Web fonts4 files, loaded late
- JavaScript780 KB of builder code
- Hero imageJPG, 1.9 MB
- Third-party tagsChat, slider, pixels
Illustrative lab figures for a sample site on a throttled mobile connection. Your audit measures your own pages and real-user data.
Sound familiar?
What problems does a penetration test solve?
A penetration test solves three common problems: “A customer's security questionnaire is holding up a deal”, “Our scanner gives us noise, not answers”, and “We shipped fast and nobody has tried to break it”. Each one has a fix.
The problem
- “A customer's security questionnaire is holding up a deal”Their security team wants a recent penetration test report and proof that findings were fixed, and you have neither ready to send.
- “Our scanner gives us noise, not answers”Scanner output is long, repetitive and full of false positives, while the real risks, such as one customer seeing another's data, go unchecked.
- “We shipped fast and nobody has tried to break it”Sign-in, permissions and APIs were built under deadline, and nobody outside the team has tested them the way an attacker would.
What changes
- Evidence for security reviewsA recent report and retest letter give your buyers' security teams the evidence they ask for.
- Real risks found and fixedAccess control, logic and configuration flaws are found by a person, fixed by your team and confirmed closed.
- Developers who know what to changeEach finding comes with steps to reproduce and a specific fix, explained on a call.
- Security that keeps paceWhere a finding can be checked automatically, we suggest a pipeline rule, so the same class of issue is caught next time.
Compare your options
Vulnerability scanner, internal review or a penetration test?
Each option suits a different situation: automated vulnerability scanner (catching known issues every build), internal developer review (reviewing changes as you ship) and Noorscale (a questionnaire, audit or launch ahead). Here's how they compare on the points buyers ask about most.
| Compared on | Automated vulnerability scanner | Internal developer review | Noorscale |
|---|---|---|---|
| Logic and access flaws | Automated vulnerability scannerUsually missed | Internal developer reviewBlind spots on your own code | NoorscaleManual testing to OWASP methods |
| How often it runs | Automated vulnerability scannerContinuously, in your pipeline | Internal developer reviewWhenever time allows | NoorscalePeriodic, deeper assurance |
| False positives | Automated vulnerability scannerMany to sort through | Internal developer reviewFew, with narrow coverage | NoorscaleEvery finding has evidence |
| Evidence for security reviews | Automated vulnerability scannerSupporting evidence only | Internal developer reviewHard to show as independent | NoorscaleReport and retest letter to share |
| Cost to start | Automated vulnerability scannerCheapest to run | Internal developer reviewDeveloper time only | NoorscaleFixed price, retest included |
| Best when | Automated vulnerability scannerCatching known issues every build | Internal developer reviewReviewing changes as you ship | NoorscaleA questionnaire, audit or launch ahead |
On the free call, Noor will tell you which option suits your stage, even when it's one of the others.
What's included
What does a penetration test include?
A penetration test includes six deliverables: scope and rules of engagement, web application testing, API testing, cloud configuration review, report and remediation plan, and retest and summary letter. Each one is working material your team can use, not a slide deck.
Scope · Penetration Testing & Security Reviews6 deliverables
- 01
Scope and rules of engagement
Targets, test accounts, timing, contacts and limits agreed and signed before testing starts, with written authorization from the system owner.
- 02
Web application testing
Manual and tool-assisted testing to the OWASP Web Security Testing Guide, covering the OWASP Top 10, including access control, authentication, session handling and injection.
- 03
API testing
REST and GraphQL APIs tested against the OWASP API Security Top 10, including object-level authorization, rate limits and excessive data exposure.
- 04
Cloud configuration review
AWS, Azure or Google Cloud accounts reviewed against CIS Benchmarks for identity, storage, networking, logging and secrets, within each provider's testing policy.
- 05
Report and remediation plan
Every finding with evidence, a CVSS risk rating, steps to reproduce and a specific fix, plus an executive summary for customers and auditors.
- 06
Retest and summary letter
Fixed findings tested again within an agreed window, with an updated report and a short letter confirming the test and retest that you can share.
Tools and platforms we work in
- BBurp Suite Professional
- ZZAP
- NNmap
- Ssqlmap
- NNuclei
- PPostman
- PProwler
- SScoutSuite
- OOWASP Web Security Testing Guide
- OOWASP API Security Top 10
- CCIS Benchmarks
- CCVSS
Process
How long does a penetration test take?
The work runs in five steps, starting in week 1. Every step ends with something you can use, so you always know what's landed and what comes next.
Time to first results: Testing window of 1 to 3 weeks
Step 01Week 1
Scope and authorize
We agree targets, environments, test accounts and timing, and get written authorization signed by the system owner.
You get: Signed scope and written authorization
Step 021 to 3 weeks
Test
Testers work through the agreed scope, report any critical issue to you straight away and keep a log of every action.
You get: Test log, critical issues flagged straight away
Step 03About 1 week after testing
Report and walk-through
You get the full report and a call with your developers to explain each finding and agree the fixes.
You get: Risk-ranked report and agreed fixes
Step 04Your timeline
Fix
Your team fixes the issues in priority order, with our help on the harder ones if you want it.
You get: Findings fixed in priority order
Step 05Within the agreed window
Retest
We test every fixed finding again and issue the updated report and summary letter.
You get: Updated report and shareable summary letter
Reporting
How will you know a penetration test is working?
You'll know a penetration test is working from four measures on a live dashboard: findings by severity, time to remediate, findings closed at retest and repeat findings. You also get a written review every month: leading indicators first, then the numbers your finance team cares about.
Monthly reportSample
- Findings by severityHigher is better
Critical, high, medium and low findings, each with a CVSS score and evidence.
- Time to remediateLower is better
Days from report to fix for each severity, against targets you set.
- Findings closed at retestHigher is better
Share of reported findings confirmed fixed when we test again.
- Repeat findingsHigher is better
Issues that reappear in later tests, a sign of a root cause still to fix.
15 minutes with Noor
Noor Khan, Founder & CEO
You'll leave with
- Your biggest growth opportunity, in plain terms
- The first two or three moves worth making
- A clear plan for your first milestone
Noor listens first, then shows you the fastest route to the result you want.
Useful to have with you
- Your website address
- The goal or problem you want to solve
- Any numbers you already track
Booking opens on Cal.com. Or send a call request
Who it's for
Who is a penetration test for?
It works best for SaaS companies answering customer security questionnaires; teams preparing for SOC 2, ISO 27001 or a large customer's vendor review; and two more listed here.
- SaaS companies answering customer security questionnaires
- Teams preparing for SOC 2, ISO 27001 or a large customer's vendor review
- Products about to launch or just through a major rebuild
- Companies on AWS, Azure or Google Cloud that want the configuration checked
Engagement
How is a penetration test scoped and priced?
Pricing is shared after the free call, in a written scope with deliverables, timeline and fee. Never a package, never a surprise.
Monthly retainer
Ongoing work against a 90-day plan, for channels that compound month over month.
- Monthly report and strategy call
- Priorities reset every quarter
- No long lock-in
- Typical for this service
Fixed-scope project
A defined scope, timeline and fee for builds, audits, migrations and launches.
Usually: Fixed-price test with one retest included
- Deliverables agreed in writing
- Milestones you can check
- Optional care plan after launch
Focused sprint
A short, time-boxed piece of work on one priority, to prove the approach first.
- One clear goal
- Working output, not a deck
- Roll into a retainer or stop
Every engagement includes
- Scope, rules of engagement and written authorization
- Web app, API and cloud configuration testing
- Risk-ranked report with a remediation plan
- Retest and shareable summary letter
What shapes the scope
- Number of apps, APIs and cloud accounts
- How many user roles to test
- Size of each API
- Testing out of hours
You'll see how each one applies to you in the written scope.
Who leads the work?
Your penetration test, led by Noor Khan
A software engineer turned AI and growth strategist. Noor sets the strategy and architecture on every engagement, reviews every plan before it ships and built the method the whole team works by.
FAQ
Questions about Penetration Testing & Security Reviews
Something else on your mind? Email grow@noorscale.com and a person will reply within one business day.
How much do penetration testing services cost?
Cost depends on the number of applications, APIs and cloud accounts in scope, how many user roles must be tested, the size of each API and whether testing has to happen out of hours. Each test is a fixed price agreed before it starts, with one retest included. You get a written scope after a free call.
How long does a penetration test take?
Testing a single web app and its API usually takes 1 to 2 weeks, with the report following about a week later. Larger scopes with several apps or cloud accounts take longer, and the dates are set out in the signed scope.
Is penetration testing safe for our live systems?
Yes, when it's planned. We agree which environments to test, use destructive techniques only with your approval, test production only at agreed times and keep a contact on call who can pause testing at any moment. A staging environment that mirrors production is often the best target.
Do you need our permission in writing?
Yes, every test runs under written authorization from the system owner and a signed scope that lists targets, dates and limits. For cloud-hosted systems we also follow the provider's penetration testing policy, and anything owned by a third party stays out of scope unless that party authorizes it too.
What's the difference between a vulnerability scan and a penetration test?
A vulnerability scan is an automated check for known issues, while a penetration test is a person actively trying to exploit weaknesses, including flaws in business logic and access control that scanners miss. Scans suit continuous checks in your pipeline, and penetration tests give periodic, deeper assurance.
Do you test to OWASP standards?
Yes, web apps are tested to the OWASP Web Security Testing Guide and the OWASP Top 10, and APIs to the OWASP API Security Top 10. Cloud configuration is checked against CIS Benchmarks, and the report maps each finding to its category.
Can we share the report with customers and auditors?
Yes, the report opens with an executive summary of scope, dates and methods for customers and auditors, followed by technical findings for your developers. After the retest you also get a summary letter you can share without exposing technical detail.
How often should we run a penetration test?
Most teams test at least once a year and after major changes, such as a new product, a rebuild or a move to a new cloud. SOC 2 and ISO 27001 programs, and many customer contracts, commonly expect regular testing with evidence that findings were fixed.
What do you need from us?
A named contact, test accounts for each user role, API documentation such as an OpenAPI file, and access to the agreed environments. For cloud reviews, a read-only role in each account is enough.
Related services
What pairs well with Penetration Testing & Security Reviews?
- Cloud & SecurityCompliance Readiness (SOC 2, ISO 27001, GDPR)Gap assessment, policies, controls and evidence ready for your auditorExplore
- Cloud & SecurityDevOps & CI/CDPipelines, containers and monitoring so releases ship safely and oftenExplore
- Websites & AppsWeb App & SaaS DevelopmentMVPs, portals and SaaS products people adoptExplore
We build Penetration Testing & Security Reviews for teams in
Free 15-minute call
Tell us about your penetration test.
In fifteen minutes you'll have a clear first step for Penetration Testing & Security Reviews and a plan to reach it. Pick a time below, or write if that's easier.
Prefer email? grow@noorscale.com
15 minutes with Noor
Noor Khan, Founder & CEO
You'll leave with
- Your biggest growth opportunity, in plain terms
- The first two or three moves worth making
- A clear plan for your first milestone
Noor listens first, then shows you the fastest route to the result you want.
Useful to have with you
- Your website address
- The goal or problem you want to solve
- Any numbers you already track
Booking opens on Cal.com. Or send a call request