Cloud, DevOps & Security
Compliance readiness for SOC 2, ISO 27001 and GDPR, with evidence your auditor can check.
For SaaS and software companies whose customers now ask for a SOC 2 report or an ISO 27001 certificate before they sign. We assess the gaps, write policies people will follow, put the technical controls in place in your cloud and tools, set up evidence collection and hand a prepared package to the independent auditor you choose.
- A person replies within one business day
- A plan you can act on
- You own every asset
- Time to first results
- Gap assessment in 2 to 3 weeks
- Audit-ready
- Typically 8 to 16 weeks, depending on gaps
- Frameworks
- SOC 2, ISO 27001 and GDPR
- Audit
- Carried out by an independent auditor you choose
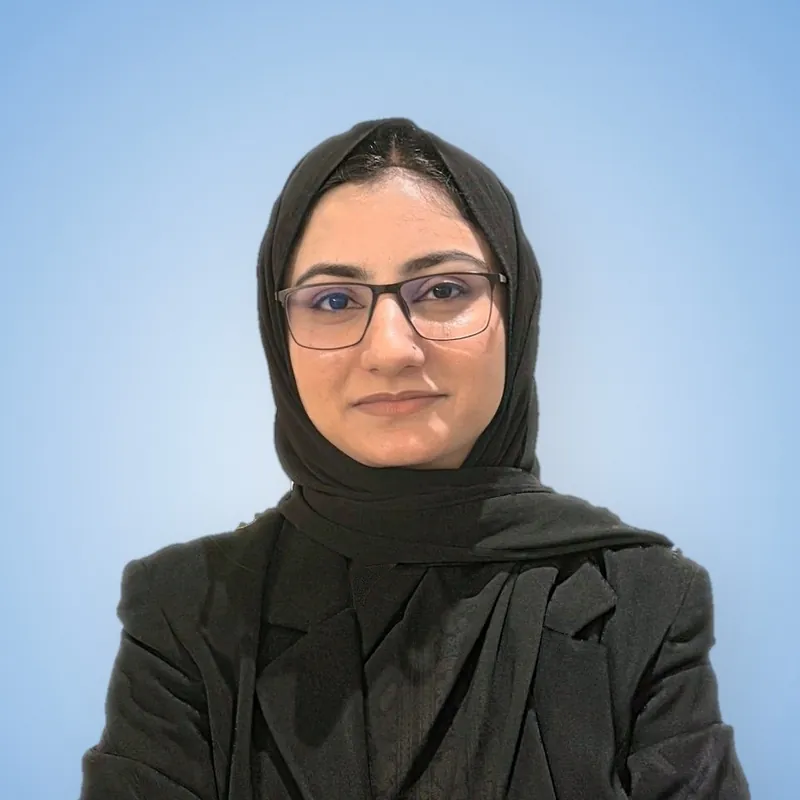 Reviewed by Noor Khan
Audit readiness· SOC 2 · evidence
SampleA gap assessment finds four SOC 2 controls missing, each is put in place, evidence for every control is collected, and the prepared package is handed to the independent auditor you choose, who issues the report.
- Gaps mapped
- Controls put in place
- Evidence collected
- Handed to your auditor
Illustration with sample data. Your version uses your accounts and numbers.
Brands Noor has worked with
Overview
What is SOC 2 compliance readiness?
SOC 2 compliance readiness is the preparation a company does before an independent CPA firm audits its controls against the AICPA Trust Services Criteria. It covers a gap assessment, policies, technical controls, evidence collection and choosing an auditor. Noorscale prepares all of this, and the same groundwork carries over to ISO 27001 and GDPR, while the report itself comes from the auditor.
See it in action
What does a SOC 2 readiness project look like when it's working?
When a SOC 2 readiness project is working, you see four changes: answers for every security questionnaire; controls that match how you work; a calm audit; and one effort, several frameworks. The live sample below is built with illustrative data. Your version runs on your own accounts and your numbers.
Site rebuild · speed and quality
SampleBefore the rebuild: performance score 38, largest contentful paint 4.9 seconds.
Back to full strength, sooner.
Same-week assessments with senior physiotherapists.
Book a visitNext available, Thursday
Same-week slots open
Sports injuries
Back and neck pain
Post-surgery rehab
Lighthouse, mobile
Template and page builderPerformance
Accessibility
Best practices
SEO
- LCPMain content visible
- 4.9 sPoor
- INPResponse to a tap
- 380 msNeeds work
- CLSLayout shift
- 0.21Needs work
Route to a bookingContact page, 7-field form
Page load waterfall
Request Largest element
- HTML document48 KB, no caching
- Stylesheets6 files, 410 KB
- Web fonts4 files, loaded late
- JavaScript780 KB of builder code
- Hero imageJPG, 1.9 MB
- Third-party tagsChat, slider, pixels
Illustrative lab figures for a sample site on a throttled mobile connection. Your audit measures your own pages and real-user data.
Sound familiar?
What problems does a SOC 2 readiness project solve?
A SOC 2 readiness project solves three common problems: “A big customer wants our SOC 2 report before they'll sign”, “We don't know which controls we're missing”, and “Our evidence lives in screenshots and memories”. Each one has a fix.
The problem
- “A big customer wants our SOC 2 report before they'll sign”The deal is close, procurement has sent a security questionnaire, and you have good practices but no report or evidence to show them.
- “We don't know which controls we're missing”Frameworks describe requirements in general terms, and nobody has mapped them to your actual cloud, code and people processes.
- “Our evidence lives in screenshots and memories”Access reviews, onboarding checks and change approvals happen some of the time, but nothing records them in a way an auditor can test.
What changes
- Answers for every security questionnairePolicies, controls and, after the audit, a report or certificate give buyers the evidence their procurement teams ask for.
- Controls that match how you workPolicies and controls are designed around your real tools and team, so they keep running after the audit.
- A calm auditEvidence is collected on schedule and checked in a mock audit before the auditor arrives.
- One effort, several frameworksControls are mapped once to SOC 2, ISO 27001 and GDPR, so each new framework builds on the last.
Compare your options
Compliance platform alone, a large advisory firm or a readiness partner?
Each option suits a different situation: compliance platform, self-run (a security lead with time); large advisory firm (many business units, full GRC program); and Noorscale (first SOC 2 for a software team). Here's how they compare on the points buyers ask about most.
| Compared on | Compliance platform, self-run | Large advisory firm | Noorscale |
|---|---|---|---|
| Evidence collection | Compliance platform, self-runStrong: automated from your tools | Large advisory firmDepends on the firm's method | NoorscalePlatform where used, owners for the rest |
| Policies | Compliance platform, self-runTemplates you adapt | Large advisory firmThorough, often extensive | NoorscaleWritten for how you work |
| Technical controls in your cloud | Compliance platform, self-runYour engineers set them up | Large advisory firmVaries by firm | NoorscalePut in place across your tools |
| Cost to start | Compliance platform, self-runLowest outside spend | Large advisory firmSized for large programs | NoorscaleFixed-price readiness project |
| Ongoing effort for your team | Compliance platform, self-runMost of the work in-house | Large advisory firmWorkshops and owner interviews | NoorscaleA few hours a week per owner |
| Best when | Compliance platform, self-runA security lead with time | Large advisory firmMany business units, full GRC program | NoorscaleFirst SOC 2 for a software team |
On the free call, Noor will tell you which option suits your stage, even when it's one of the others.
What's included
What does a SOC 2 readiness project include?
A SOC 2 readiness project includes six deliverables: scope and gap assessment, policies and procedures, technical controls, evidence collection, GDPR records and processes, and auditor handoff and audit support. Each one is working material your team can use, not a slide deck.
Scope · Compliance Readiness (SOC 2, ISO 27001, GDPR)6 deliverables
- 01
Scope and gap assessment
Systems and Trust Services Criteria, or ISO 27001 Annex A controls, agreed for scope, then your current practices compared against them, with a ranked remediation plan.
- 02
Policies and procedures
Information security, access control, change management, incident response, vendor management and the other required policies, written to match how you actually work.
- 03
Technical controls
Single sign-on and MFA, least-privilege access, logging, encryption, backups, vulnerability management and change control put in place across your cloud, code and tools.
- 04
Evidence collection
Automated evidence through a platform such as Vanta, Drata or Secureframe where you use one, plus a named owner and schedule for every manual control.
- 05
GDPR records and processes
Records of processing activities, data protection impact assessments where needed, data processing agreements and a process for data subject requests.
- 06
Auditor handoff and audit support
Help shortlisting independent auditors, a readiness review before fieldwork, and support answering auditor requests during the audit.
Tools and platforms we work in
- VVanta
- DDrata
- SSecureframe
 AWS Security Hub
- AWS Config
- MMicrosoft Defender for Cloud
 Google Security Command Center
- OOkta
- MMicrosoft Entra ID
- Google Workspace
- JJira
 GitHub
Process
How long does a SOC 2 readiness project take?
The work runs in five steps, starting in weeks 1 to 3 and finishing in weeks 12 to 16. Every step ends with something you can use, so you always know what's landed and what comes next.
Time to first results: Gap assessment in 2 to 3 weeks
Step 01Weeks 1 to 3
Scope and assess
We agree the framework, systems and criteria in scope, interview control owners and compare what exists against each requirement.
You get: Gap assessment and ranked remediation plan
Step 02Weeks 3 to 6
Policies and control design
Policies written and approved, and each control designed with an owner, a frequency and the evidence it produces.
You get: Approved policies and designed controls
Step 03Weeks 4 to 12
Implement controls and evidence
Technical controls rolled out in your cloud and tools, evidence collection connected and each owner trained on their part.
You get: Controls live and evidence collection connected
Step 04Weeks 10 to 14
Readiness review
A mock audit walks through every control and its evidence, and the remaining gaps are closed.
You get: Mock audit results and closed gaps
Step 05Weeks 12 to 16
Auditor handoff
We hand the package to your chosen auditor and support you through fieldwork, then help keep controls running for the next period.
You get: Prepared package with your chosen auditor
Reporting
How will you know a SOC 2 readiness project is working?
You'll know a SOC 2 readiness project is working from four measures on a live dashboard: controls in place, evidence on schedule, open gaps by risk and auditor requests answered. You also get a written review every month: leading indicators first, then the numbers your finance team cares about.
Monthly reportSample
- Controls in placeHigher is better
Share of in-scope controls designed, implemented and producing evidence.
- Evidence on scheduleHigher is better
Controls with current evidence collected on time, ready for the auditor.
- Open gaps by riskHigher is better
Gaps from the assessment still open, ranked by risk, tracked down to zero before the audit.
- Auditor requests answeredHigher is better
Requests from the auditor answered on time during fieldwork.
15 minutes with Noor
Noor Khan, Founder & CEO
You'll leave with
- Your biggest growth opportunity, in plain terms
- The first two or three moves worth making
- A clear plan for your first milestone
Noor listens first, then shows you the fastest route to the result you want.
Useful to have with you
- Your website address
- The goal or problem you want to solve
- Any numbers you already track
Booking opens on Cal.com. Or send a call request
Who it's for
Who is a SOC 2 readiness project for?
It works best for SaaS companies whose customers ask for a SOC 2 report; software firms selling to enterprise, financial services or healthcare buyers; and two more listed here.
- SaaS companies whose customers ask for a SOC 2 report
- Software firms selling to enterprise, financial services or healthcare buyers
- Teams pursuing ISO 27001 certification alongside or instead of SOC 2
- Companies handling personal data that need their GDPR records in order
Engagement
How is a SOC 2 readiness project scoped and priced?
Pricing is shared after the free call, in a written scope with deliverables, timeline and fee. Never a package, never a surprise.
Monthly retainer
Ongoing work against a 90-day plan, for channels that compound month over month.
- Monthly report and strategy call
- Priorities reset every quarter
- No long lock-in
- Typical for this service
Fixed-scope project
A defined scope, timeline and fee for builds, audits, migrations and launches.
Usually: Fixed-price readiness project, then optional monthly compliance support
- Deliverables agreed in writing
- Milestones you can check
- Optional care plan after launch
Focused sprint
A short, time-boxed piece of work on one priority, to prove the approach first.
- One clear goal
- Working output, not a deck
- Roll into a retainer or stop
Every engagement includes
- Scope and gap assessment with a remediation plan
- Policies, procedures and control design
- Technical controls and evidence collection set up
- Readiness review and auditor handoff
What shapes the scope
- Company size and systems in scope
- Trust Services Criteria included
- How many controls already exist
- Adding ISO 27001 or GDPR
You'll see how each one applies to you in the written scope.
Who leads the work?
Your SOC 2 readiness project, led by Noor Khan
A software engineer turned AI and growth strategist. Noor sets the strategy and architecture on every engagement, reviews every plan before it ships and built the method the whole team works by.
FAQ
Questions about Compliance Readiness (SOC 2, ISO 27001, GDPR)
Something else on your mind? Email grow@noorscale.com and a person will reply within one business day.
How much does SOC 2 compliance readiness cost?
Cost depends on your size, how many systems are in scope, which Trust Services Criteria you include, how many controls already exist and whether you add ISO 27001 or GDPR. Readiness is a fixed-price project, while the audit fee is paid directly to the independent auditor and compliance platforms bill you separately. You get a written scope after a free call.
Does Noorscale issue the SOC 2 report or ISO 27001 certificate?
The report and certificate come from independent bodies: a licensed CPA firm issues SOC 2 reports, and an accredited certification body issues ISO 27001 certificates. We prepare the controls, policies and evidence they examine and support you through the audit, which keeps the assessment independent, as both frameworks require.
What's the difference between SOC 2 Type 1 and Type 2?
A Type 1 report checks whether your controls are designed properly at a single point in time. A Type 2 report checks whether they actually operated over an observation period, usually 3 to 12 months. Many companies start with Type 1 to answer customers sooner, then move to Type 2.
How long does SOC 2 readiness take?
Most companies are ready for a Type 1 audit in 8 to 16 weeks, depending on how many gaps the assessment finds and how quickly owners can act. A Type 2 audit then needs an observation period of several months before the auditor reports.
Should we choose SOC 2 or ISO 27001?
Choose the one your customers ask for. SOC 2 is a common request from buyers who expect an AICPA attestation report, while ISO 27001 is a certification recognized worldwide that many enterprises and public bodies prefer. The controls overlap heavily, so we design them once and map them to both.
Do we need a compliance platform such as Vanta or Drata?
It helps, and it's optional. Platforms such as Vanta, Drata and Secureframe collect evidence from your cloud and tools automatically and track every control in one place. For a small scope, a well-organized evidence folder with owners and a schedule can work, and we'll recommend based on your size and audit plans.
How does GDPR readiness fit in?
GDPR readiness covers how you collect, use and protect personal data: records of processing, a lawful basis for each use, data processing agreements, impact assessments where needed and a process for access and deletion requests. Many SOC 2 and ISO 27001 controls support it, so we build them together. Legal interpretation stays with your counsel or data protection officer.
What do you need from our team?
A sponsor who can approve policies and decisions, an owner for each area such as engineering, IT and HR, and admin access to the systems in scope. Most owners spend a few hours a week during implementation, while we handle drafting, configuration and evidence setup.
Can you keep us compliant after the audit?
Yes, on a monthly retainer we run the recurring controls with you, such as access reviews, vendor reviews and policy updates, keep evidence current and prepare you for the next audit period. That keeps a Type 2 observation window clean.
Related services
What pairs well with Compliance Readiness (SOC 2, ISO 27001, GDPR)?
- Cloud & SecurityPenetration Testing & Security ReviewsAuthorized testing of web apps, APIs and cloud, with fixes retestedExplore
- Cloud & SecurityCloud MigrationStrategy, landing zones and migration to AWS, Azure or Google CloudExplore
- AI AgentsPrivate & In-Region AIOpen-weight LLMs on your own cloud or hardware, data kept in regionExplore
We build Compliance Readiness (SOC 2, ISO 27001, GDPR) for teams in
Free 15-minute call
Tell us about your SOC 2 readiness project.
In fifteen minutes you'll have a clear first step for Compliance Readiness (SOC 2, ISO 27001, GDPR) and a plan to reach it. Pick a time below, or write if that's easier.
Prefer email? grow@noorscale.com
15 minutes with Noor
Noor Khan, Founder & CEO
You'll leave with
- Your biggest growth opportunity, in plain terms
- The first two or three moves worth making
- A clear plan for your first milestone
Noor listens first, then shows you the fastest route to the result you want.
Useful to have with you
- Your website address
- The goal or problem you want to solve
- Any numbers you already track
Booking opens on Cal.com. Or send a call request